Summary
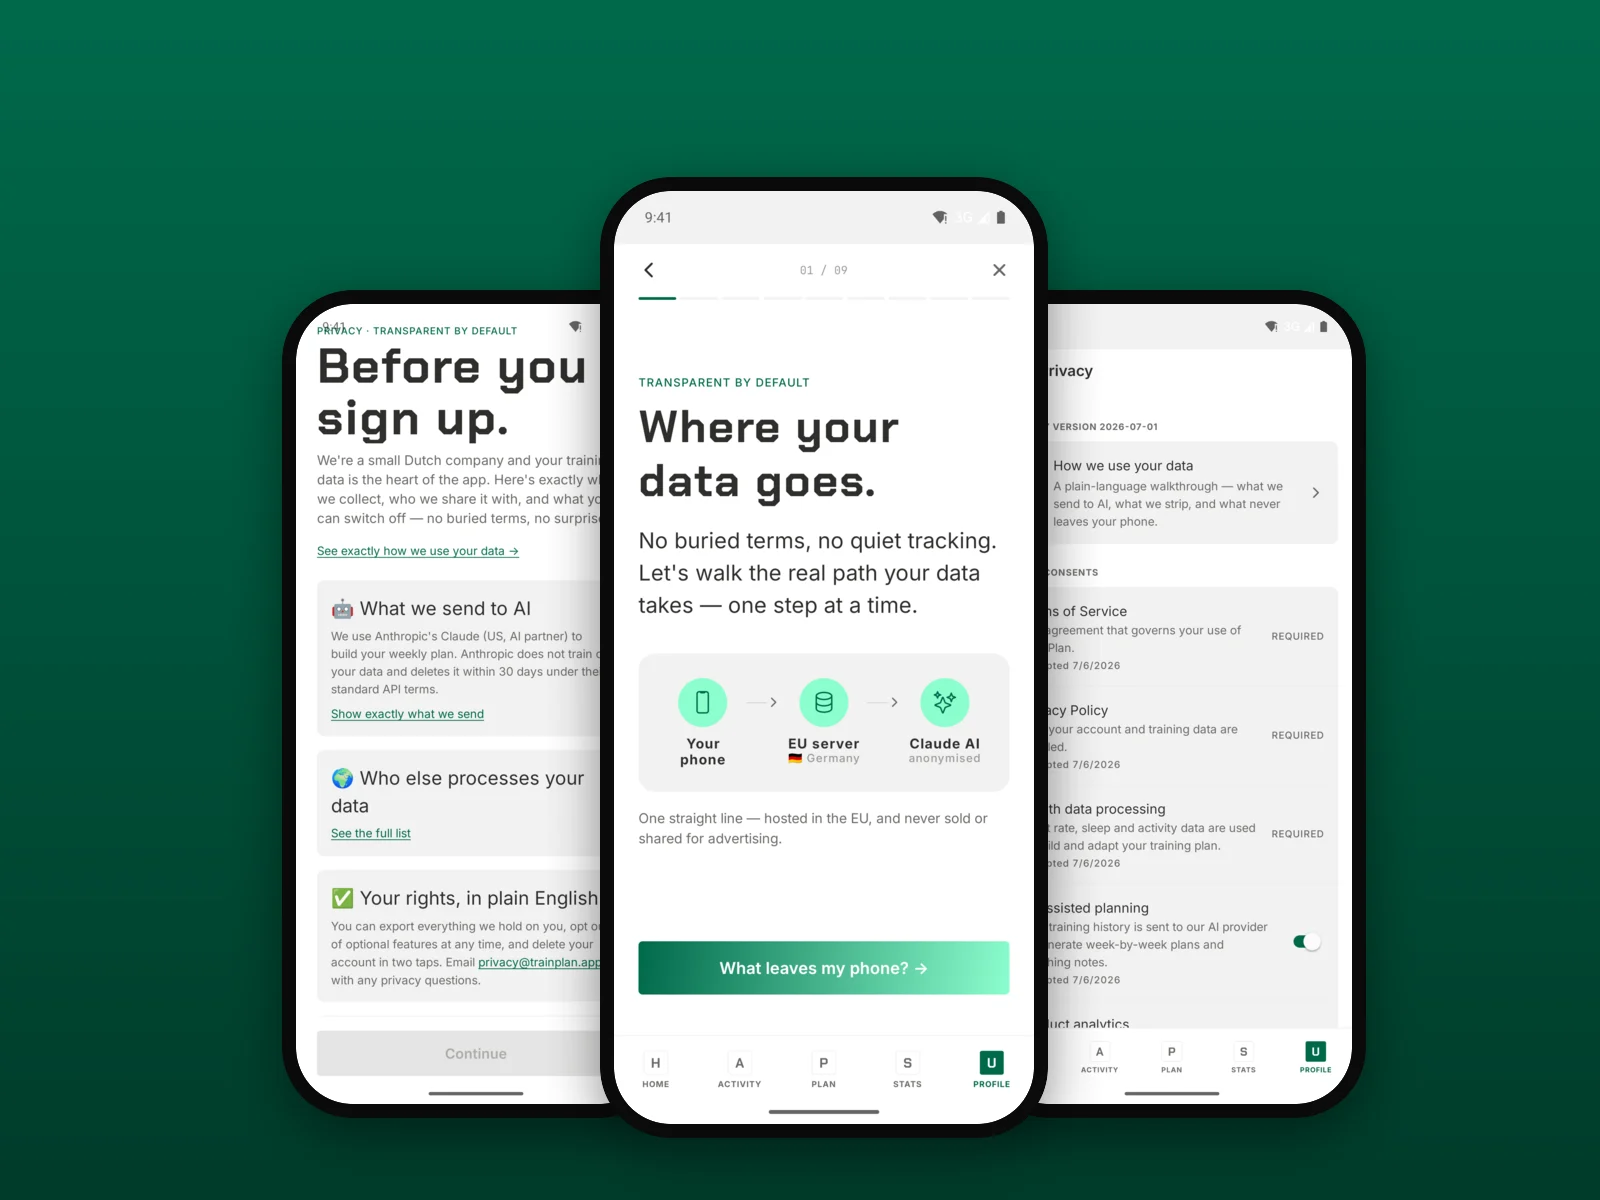
- All data encrypted at rest (AES-256) and in transit (TLS 1.2+)
- EU-hosted infrastructure [TODO: confirm region — AWS Frankfurt, OVHcloud, or equivalent]
- No health data used for advertising, training of general-purpose models, or sale to third parties
- Automatic account deletion 90 days after subscription end
- 72-hour breach notification per GDPR Article 33
Authentication
TrainPlan authentication is delegated to Apple ID and Google. We never store your password. We never handle your payment card — Apple and Google do.
Data encryption
Training data, plan history, and personal profile details are encrypted at rest with AES-256 using keys managed by [TODO: KMS provider — typically AWS KMS or GCP KMS]. In transit, all traffic uses TLS 1.2 or higher; older versions are refused at the load balancer.
Access controls
Production access is limited to the engineering team and protected by hardware-key 2FA. Production access events are logged and reviewed weekly. No engineer has long-lived direct database access.
Third-party services (sub-processors)
[TODO: complete table — each row should list the sub-processor, the data category they process, their hosting region, and a link to their DPA. Update this list with material version bumps.]
Backups and recovery
Encrypted backups of production data are taken daily and retained for [TODO: 30 days or per your policy]. Recovery playbooks are tested quarterly. Backup encryption keys are rotated annually.
Vulnerability disclosure
If you’ve found a security issue, email security@trainplan.app. We respond within two working days, disclose responsibly per a 90-day timeline, and acknowledge reporters in our changelog unless you prefer otherwise.
Certifications
[TODO: list any certifications. SOC 2 Type II, ISO 27001, or similar if applicable. If none yet, a “planned for [quarter]” line is better than silence.]
Questions
Security questions: security@trainplan.app. Data-handling questions: privacy@trainplan.app.